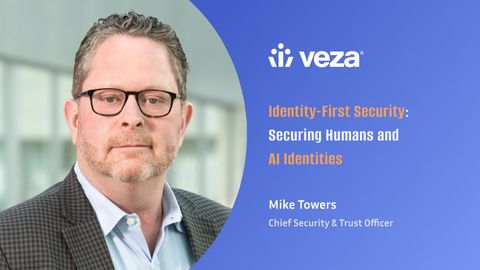
Every AI agent becomes an identity needing governance.
Mike Towers has built his security playbook around spotting shifts in identity, trust, and enterprise risk across global pharma, cloud, and AI-driven environments. He reveals how to lead identity-first security programs, enable digital trust as a business enabler, and why managing human and non-human identities is the ultimate edge for next-generation security leaders.
The shift from perimeter-based to identity-based security fundamentally changed how I approach risk. When I was CISO at pharmaceutical companies, we realized our traditional castle-and-moat defenses were meaningless when a single compromised credential could access crown jewel IP from anywhere. This drove home that identity isn't just an IT function—it's the new perimeter. Every security decision now starts with "who has access to what and why?"
Digital trust is becoming the foundation of business velocity. At my previous companies, we couldn't accelerate drug development or enable remote clinical trials without proving we could protect patient data. Today, enterprises can't adopt AI, enable partners, or complete M&A without demonstrating control over access. Trust isn't about saying "no"—it's about enabling the business to confidently say "yes" to innovation while managing risk transparently.
Success comes from starting with visibility, not control. Early in my career, I tried to implement strict access controls before understanding our permission landscape—it failed spectacularly. The breakthrough came when we first mapped who could access what across all systems, then used that intelligence to drive controls. Also critical: don't treat identity as a technical project. It's a business transformation that requires executive sponsorship and clear value metrics.
Non-human identities often outnumber human ones 45-to-1 and have more privileged access, yet most organizations can't even inventory them. Enterprises need to apply the same rigor to machine identities as human ones: know what exists, understand their permissions, and enforce least privilege. At Veza, we've seen clients discover AI tools with production database access they didn't know about. The key is treating all identities—human or machine—as potential risk vectors requiring continuous governance.
Accuracy comes from understanding effective permissions, not just assigned roles. Traditional IAM shows you group memberships; we show what someone can actually do with their access. For joiners, we enable role mining based on peer analysis. For movers, we automatically flag permissions that no longer align with their new role. For leavers, we trace access paths across all connected systems. The magic is continuous monitoring—access drift happens daily, not just during major transitions.
Three principles guide me: First, clarity of mission—everyone should understand how their work protects the business. Second, psychological safety—in security, people must feel safe reporting mistakes or near-misses. Third, celebrate learnings over blame. During one transformation, we turned a major incident into our best training tool by focusing on systematic improvements rather than finding fault. When teams see leaders admit mistakes and focus on solutions, they become more innovative and resilient.
Life sciences taught me that your most sensitive data is often in the hands of third parties—CROs, manufacturing partners, research collaborators. This external access challenge exists everywhere now. The key lesson: you can't secure what you can't see, and visibility must extend beyond your four walls. Also, regulatory compliance in pharma showed me that good security practices often become tomorrow's compliance requirements—get ahead of the curve.
AI will multiply the identity challenge exponentially; every AI agent becomes an identity needing governance. But AI also offers solutions: imagine AI-driven access reviews that understand context and risk, not just checkboxes. Enterprises should start by establishing visibility into all identities today, because you can't govern AI-driven access if you don't understand human-driven access. The winners will use AI to make access decisions more intelligent while maintaining human oversight for critical risks.
Mike Towers is the Chief Security & Trust Officer at Veza, where he leads the company’s cybersecurity and data protection strategy. He oversees Veza’s Advisory Board, advances its identity security capabilities, and ensures customers understand the unique value of Veza’s industry-leading identity security and intelligent access platform. Mike’s team works to safeguard Veza’s platform and help customers address complex access control challenges that come with digital and cloud expansion.
As the founder of Digital Trust Group LLC and a seasoned executive, Mike specializes in digital security, trust, and business resiliency. Prior to Veza, he served as Takeda’s Chief Digital Trust Officer and held leadership roles at Allergan and GSK, where he built robust security frameworks. Over his career, he has influenced more than 50 M&A deals and was inducted into the CSO Hall of Fame. A respected speaker, author, and board advisor, Mike continues to champion responsible innovation, data protection, and knowledge sharing. Based in Boston, he remains a leading voice in advancing digital trust and security.
More about Mike: 
Veza is the leader in identity security, helping organizations secure access across the enterprise. Veza’s Access Platform goes beyond identity governance and administration (IGA) tools to visualize, monitor, and control entitlements so that organizations can stay compliant and achieve least privilege. Global enterprises like Wynn Resorts, Expedia, and Blackstone trust Veza to manage identity security use cases, including privileged access monitoring, non-human identity (NHI) security, access entitlement management, data system access, SaaS access security, IAM hygiene, identity security posture management (ISPM), and next-generation IGA. Founded in 2020, Veza is headquartered in Los Gatos, California, and is funded by Accel, Bain Capital, Ballistic Ventures, Google Ventures (GV), NEA, Norwest Venture Partners, and True Ventures. Visit us at www.veza.com and follow us on LinkedIn, X, and YouTube.
Tell others what you think of TechIntelPro.


 Rate us on G2